
macOS 27.2 Golden Gateでも、引き続きcurlなどにeMudhraの証明書検証問題が残っているので注意してください。詳細は以下から。
Appleは現地時間2026年10月22日、電子証明書を発行するインドの認証局eMudhraが2025年04月30日に中間CA証明書の鍵を生成したさい、不備により暗号的に弱い鍵が生成&公開されていたことに関し、SafariやMailなどAppleのネットワークやセキュリティフレームワークを使用するアプリにおいてeMudhraの中間CA証明書をブロックを開始したと発表し、
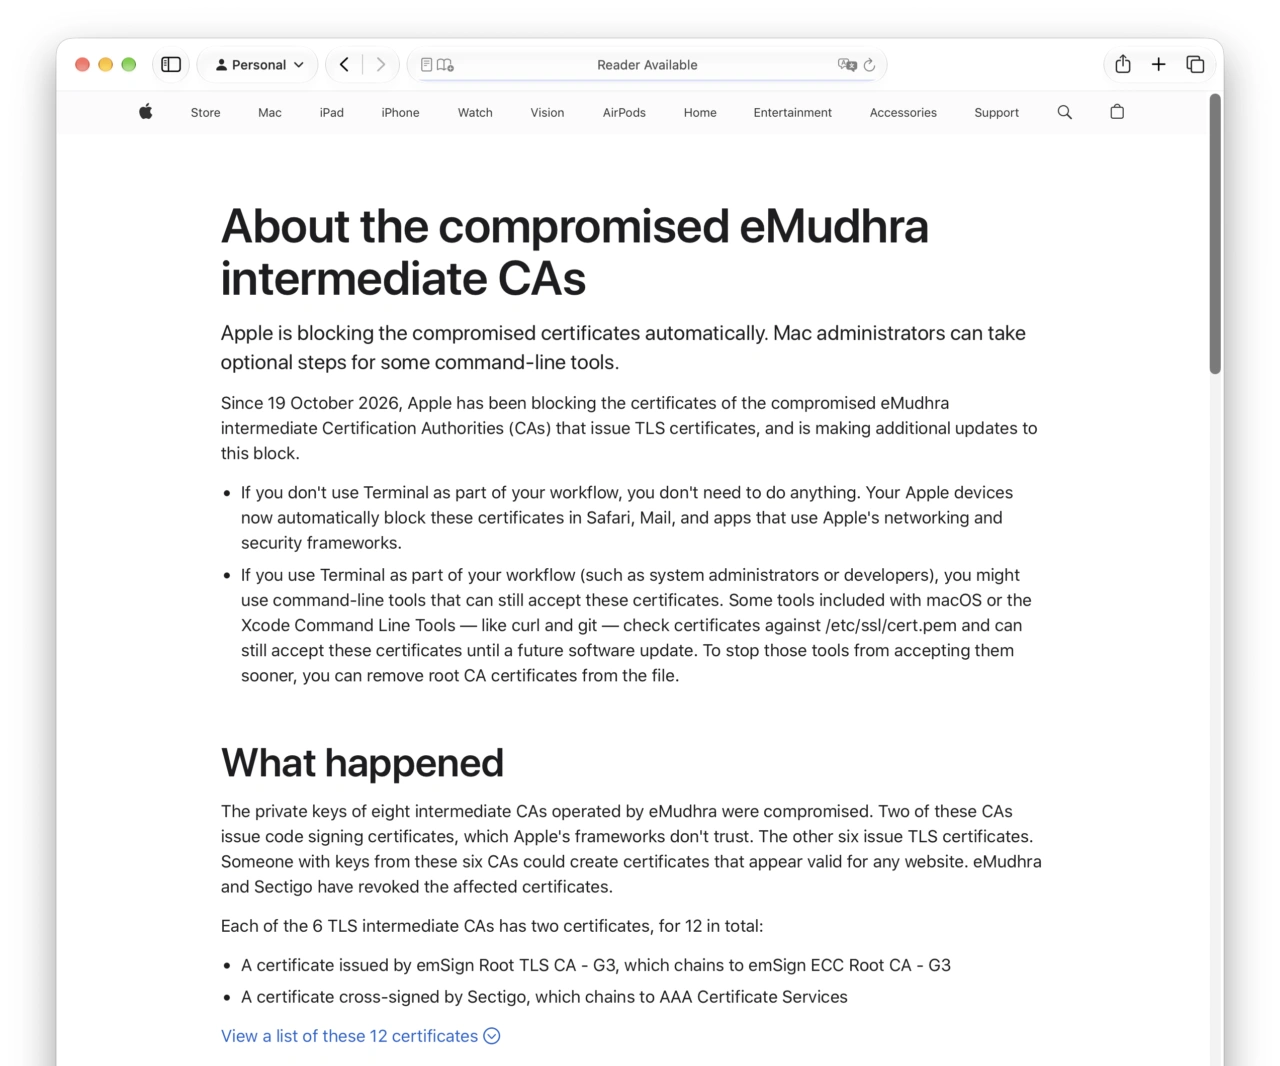
Since 19 October 2026, Apple has been blocking the certificates of the compromised eMudhra intermediate Certification Authorities (CAs) that issue TLS certificates, and is making additional updates to this block.
About the compromised eMudhra intermediate CAs – Apple Support
同時に、今後のアップデートで問題が修正されるまでmacOSのコマンドラインツールやcurlやgit, python3, ruby, perl, opensslなどを含むXcode Command Line Toolsが使用する”/etc/ssl/cert.pem”から問題の証明書につながるルートCA証明書を削除するように開発者やシステム管理者に通知していましたが、この問題は現地時間2026年10月26日にリリースされた「macOS 27.2 Golden Gate (26B123)」では修正されていませんでした。
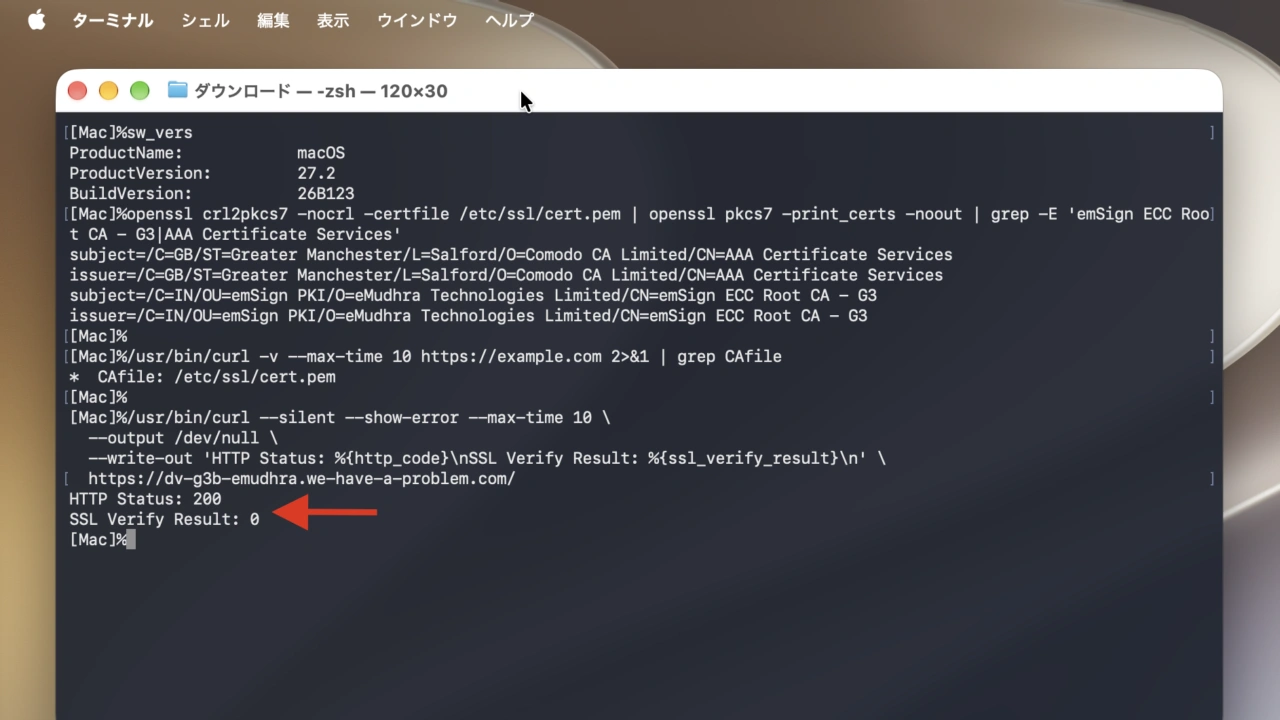
元AppleのDaniel HooperさんやJamfメンバーによると、Appleは今後のアップデートでこの問題を修正すると発表していたものの、macOS 27.2 Golden Gateのcert.pemにもeMudhra関連のルートCA証明書(AAA Certificate Services/emSign ECC Root CA – G3)が引き続き存在し、macOSデフォルトのcurlがeMudhraの問題のあるTLS証明書を信頼している事が確認できたので、コマンドラインツールを利用するシステム管理者や開発者の方は、Appleがパッチを提供するまで公式に案内されている暫定的な回避策を行っておくことをオススメします。
macOS Developers should update their /etc/ssl/cert.pem file to remove the compromised eMudhra certificate.
Apple has directions here: https://t.co/qKOhtfHNst https://t.co/mFrm6o9rXC
— Daniel Hooper (@DanielcHooper) October 26, 2026
Updated to macOS 27.2, and it’s still using the compromised eMudhra CA. Hey @Apple, make this priority, please. https://t.co/ucR5SFLRsX
— junian.dev (@JunianDev) October 27, 2026
- About the compromised eMudhra intermediate CAs – Apple Support
コメント